Want to bookmark your favourite articles and stories to read or reference later? Start your Independent Membership today.
Already a member?
Log in
Data storage firm Snowflake has said a cybersecurity breach at Asos was not caused by a vulnerability or flaw with its platform.
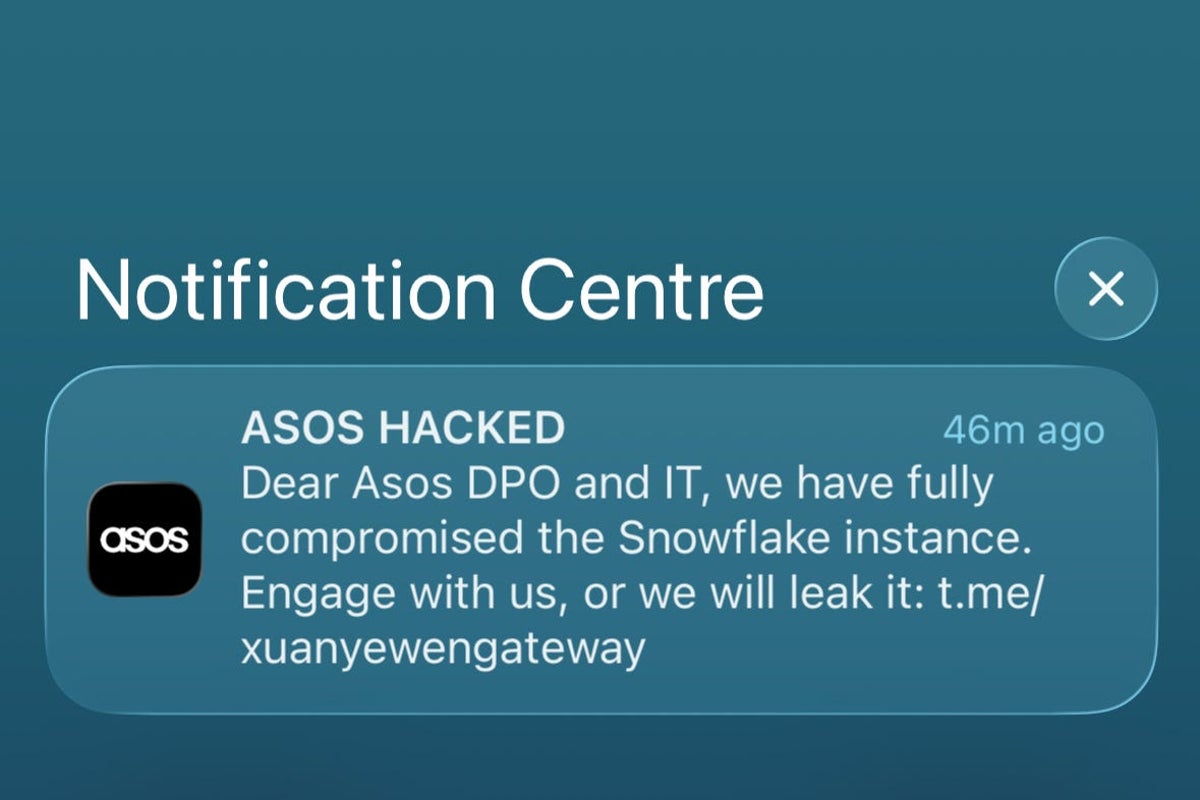
On Tuesday, Asos customers received a phone alert saying that the retailer had been hacked, which claimed Snowflake had been compromised.
The message read: “Dear ASOS DPO and IT, we have fully compromised the Snowflake instance. Engage with us, or we will leak it,” followed by a Telegram link.
The fast fashion retailer said the cyber attacker gained access to some personal data, including names and contact details.
They were also able to access “certain non-personal account-related information”, Asos said.
Asos said on Thursday it has undertaken a detailed investigation over the past 48 hours and found an “unauthorised party gained access to an Asos employee account by impersonating a trusted contact to obtain log-in credentials”.
It said the party then used the credentials to access information on third-party platforms used by Asos.
On Friday, Snowflake – a US cloud-based AI data storage business – distanced itself from the incident after investigations, despite being referenced in the message from the hackers.
A Snowflake spokeswoman said: “We are aware of Asos’s notification to their customers regarding this incident.
“We can confirm this issue did not in any way result from a vulnerability, weakness, flaw, or misconfiguration with the Snowflake service, platform, or internal environments, and was not caused by Snowflake.
“No remediation is required for Snowflake customers.
“We continue to encourage adherence to our security best practices.”
Asos stressed that no payment card information or account passwords were accessed.
The Asos website and app were safe to use throughout the incident and “remain safe” to use, the firm said.
It said: “There is no action you need to take on your account.
“However, please remain cautious of unexpected messages or calls claiming to be from Asos.
“We will never ask you to share passwords, security codes or payment details through an unsolicited message or call.”